There’s a common misconception in security procurement: that signing a contract with a Managed Security Service Provider (MSSP) transfers not just the work, but the accountability. It doesn’t. Your MSSP manages your security. You own it. In 2026, with threat actors moving faster, regulatory scrutiny
There is a tempting logic in the idea of assessing your own security posture. Your internal team knows the environment, understands the history of decisions made, and can move quickly without the overhead of onboarding an outside party. So why bring in someone from outside? Why pay for the privilege
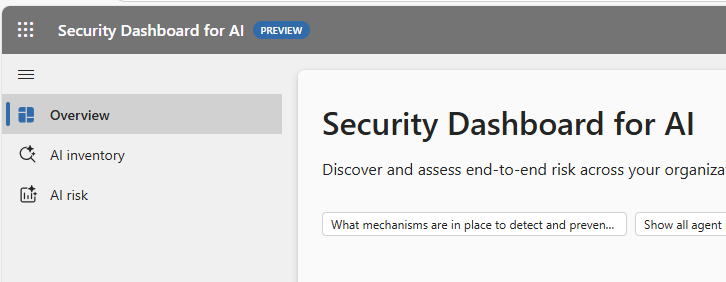
The missing control plane for AI risk across Entra, Defender, and Purview Microsoft has quietly shipped one of the most important security capabilities for the AI era. The new Security Dashboard for AI in Microsoft 365 is now in public preview, and it solves a real problem most organisations already
Questionnaires are theatre. Real risk reduction looks very different. Third-party risk keeps showing up in breach reports, regulator findings, and insurance claims. Yet most organisations still manage it with long questionnaires, annual reviews, and a false sense of control. This is not a tooling pr
AI is not breaking cybersecurity. Weak identity controls are. AI just makes the consequences faster, cheaper, and harder to ignore. Right now, too many security strategies are being reshaped around AI threats while the same organisations still run fragile identity and access management systems. This
Third-party risk is now one of the biggest blind spots in UK cyber security. Most attacks still land through simple things like phishing and poor patching, but when something really disruptive happens, a supplier is often involved somewhere in the chain. Government and NCSC-aligned data backs this u
More and more organisations increasingly rely on ecosystems of connected applications and integrations to drive business value. However, the recent incident involving Salesforce and a third-party app vendor underscores a sobering reality: the attack surface has extended well beyond the core platform
Incident Overview On Tuesday 18 November 2025, Cloudflare experienced a significant global outage that disrupted access to multiple high-profile web services and applications. The company, which handles approximately 20 % of the world’s web traffic reported that the root cause was a configuration fi
Source: https://publications.parliament.uk/pa/bills/cbill/59-01/0329/240329.pdf The UK government has published the Bill to overhaul and extend the regulatory regime for network and information systems (NIS) in the UK. At its heart the Bill amends the Network and Information Systems Regulations 2018
On 15 October 2025, the UK Information Commissioner’s Office (ICO) imposed a combined £14 million penalty on outsourcing giant Capita plc and Capita Pension Solutions Limited for serious data protection failings linked to its 2023 cyber-attack. The ICO split the fine into £8m for Capita plc and £6m
So, DCC is not just a one-off audit per contract; it’s a forward-looking assurance mechanism to streamline supplier cyber assurance across multiple contracts, reduce duplication, and raise baseline cyber maturity in the defence supply chain. The Four Levels of DCC There are four levels (0 to 3) unde
Introduction Your organisation’s email domain is more than just an address it’s an extension of your brand, your reputation, and your trustworthiness in the digital world. Unfortunately, cybercriminals know this too. Fraudsters frequently register similar or deceptive domain names to impersonate leg