UtopianKnight Consultancy Limited is proud to have signed the UK Cyber Resilience Pledge. The UK Cyber Resilience Pledge is a voluntary government scheme, announced by the Security Minister on 22 April 2026 at CyberUK in Glasgow, asking businesses to strengthen their cyber defences. Over 60 organisa
There is a tempting logic in the idea of assessing your own security posture. Your internal team knows the environment, understands the history of decisions made, and can move quickly without the overhead of onboarding an outside party. So why bring in someone from outside? Why pay for the privilege
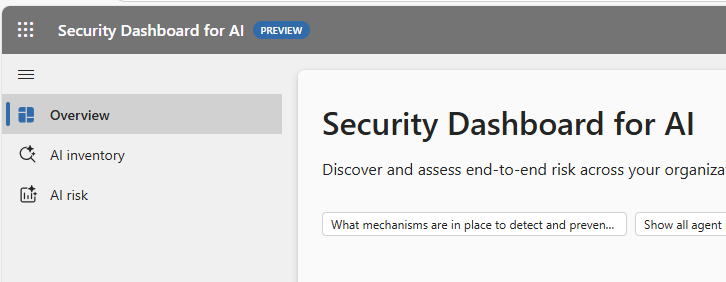
The missing control plane for AI risk across Entra, Defender, and Purview Microsoft has quietly shipped one of the most important security capabilities for the AI era. The new Security Dashboard for AI in Microsoft 365 is now in public preview, and it solves a real problem most organisations already
Questionnaires are theatre. Real risk reduction looks very different. Third-party risk keeps showing up in breach reports, regulator findings, and insurance claims. Yet most organisations still manage it with long questionnaires, annual reviews, and a false sense of control. This is not a tooling pr
AI is not breaking cybersecurity. Weak identity controls are. AI just makes the consequences faster, cheaper, and harder to ignore. Right now, too many security strategies are being reshaped around AI threats while the same organisations still run fragile identity and access management systems. This
Third-party risk is now one of the biggest blind spots in UK cyber security. Most attacks still land through simple things like phishing and poor patching, but when something really disruptive happens, a supplier is often involved somewhere in the chain. Government and NCSC-aligned data backs this u
In November 2025, CrowdStrike publicly announced that it had terminated an insider who leaked screenshots of internal dashboards to a hacker collective. While CrowdStrike maintains its systems were not compromised and customer data was unaffected, the incident highlights a critical truth: insider th
More and more organisations increasingly rely on ecosystems of connected applications and integrations to drive business value. However, the recent incident involving Salesforce and a third-party app vendor underscores a sobering reality: the attack surface has extended well beyond the core platform
Incident response exercises are no longer a luxury for large enterprises. They are a practical necessity for organisations of every size. Cyber incidents remain one of the most disruptive events a business can face. They create operational downtime, financial loss, reputational damage, and regulator
Artificial intelligence has rapidly become one of the most transformative forces in technology. It has disrupted how organisations operate, how decisions are made, and how data is processed at scale. Cyber security has always adapted to change, yet the rise of generative AI has created a shift unlik
Source: https://publications.parliament.uk/pa/bills/cbill/59-01/0329/240329.pdf The UK government has published the Bill to overhaul and extend the regulatory regime for network and information systems (NIS) in the UK. At its heart the Bill amends the Network and Information Systems Regulations 2018
In October 2025, one of the most significant supply-chain-adjacent cybersecurity incidents in recent years came to light: the Seattle-based network security and application-delivery firm F5 admitted that a “highly sophisticated nation-state threat actor” had achieved long-term unauthorised access to